Linux安全性PHP木马检测和预防
电脑杂谈 发布时间:2020-08-05 08:06:19 来源:网络整理
1. 服务器自身的系统安全性:
使用最新的操作系统或最新的稳定版本(例如Ubuntu的LTS)定期更新系统,合理划分系统权限并保护重要文件.
例如:
  # chattr +i /etc/passwd
  # chattr +i /etc/group
  # chattr +i /etc/shadow
  # chattr +i /etc/gshadow
  # chattr +i /etc/ssh/sshd_config
使用DenyHost程序防止SSH受到暴力攻击. 有关具体方法,请参阅场外文章:
2. Web服务器和PHP安全规则:

首先根据需要更新Web服务器和PHP,严格定义网站程序目录中的权限,例如,禁止在不会被修改的地方具有写权限,并且需要临时目录(例如上载目录和缓存)限制PHP或相关脚本.
与nginx规则有关的脚本:
location ~ .*\.(php|php5)?$ {
  rewrite ^/(uc\_client|templates|include|plugins|admin|attachments|images|
  forumdata)/.*\.(php|php5)?$ /50x.php last;
}
与Apache规则相关的脚本
//注意: 将其更改为您需要阻止的目录,例如上载目录
php_flag引擎关闭
允许订单,拒绝
所有人拒绝
需要在php.ini中进行哪些修改
搜索: 发现disable_functions并在=之后添加. 这是禁止在php中执行的功能
exec,system,passthru,error_log,ini_alter,dl,openlog,syslog,readlink,symlink,link,leak,fsockopen,proc_open,
popepassthru,chroot,scandir,chgrp,chown,escapeshellcmd,escapeshellarg,shell_exec,proc_get_status,popen
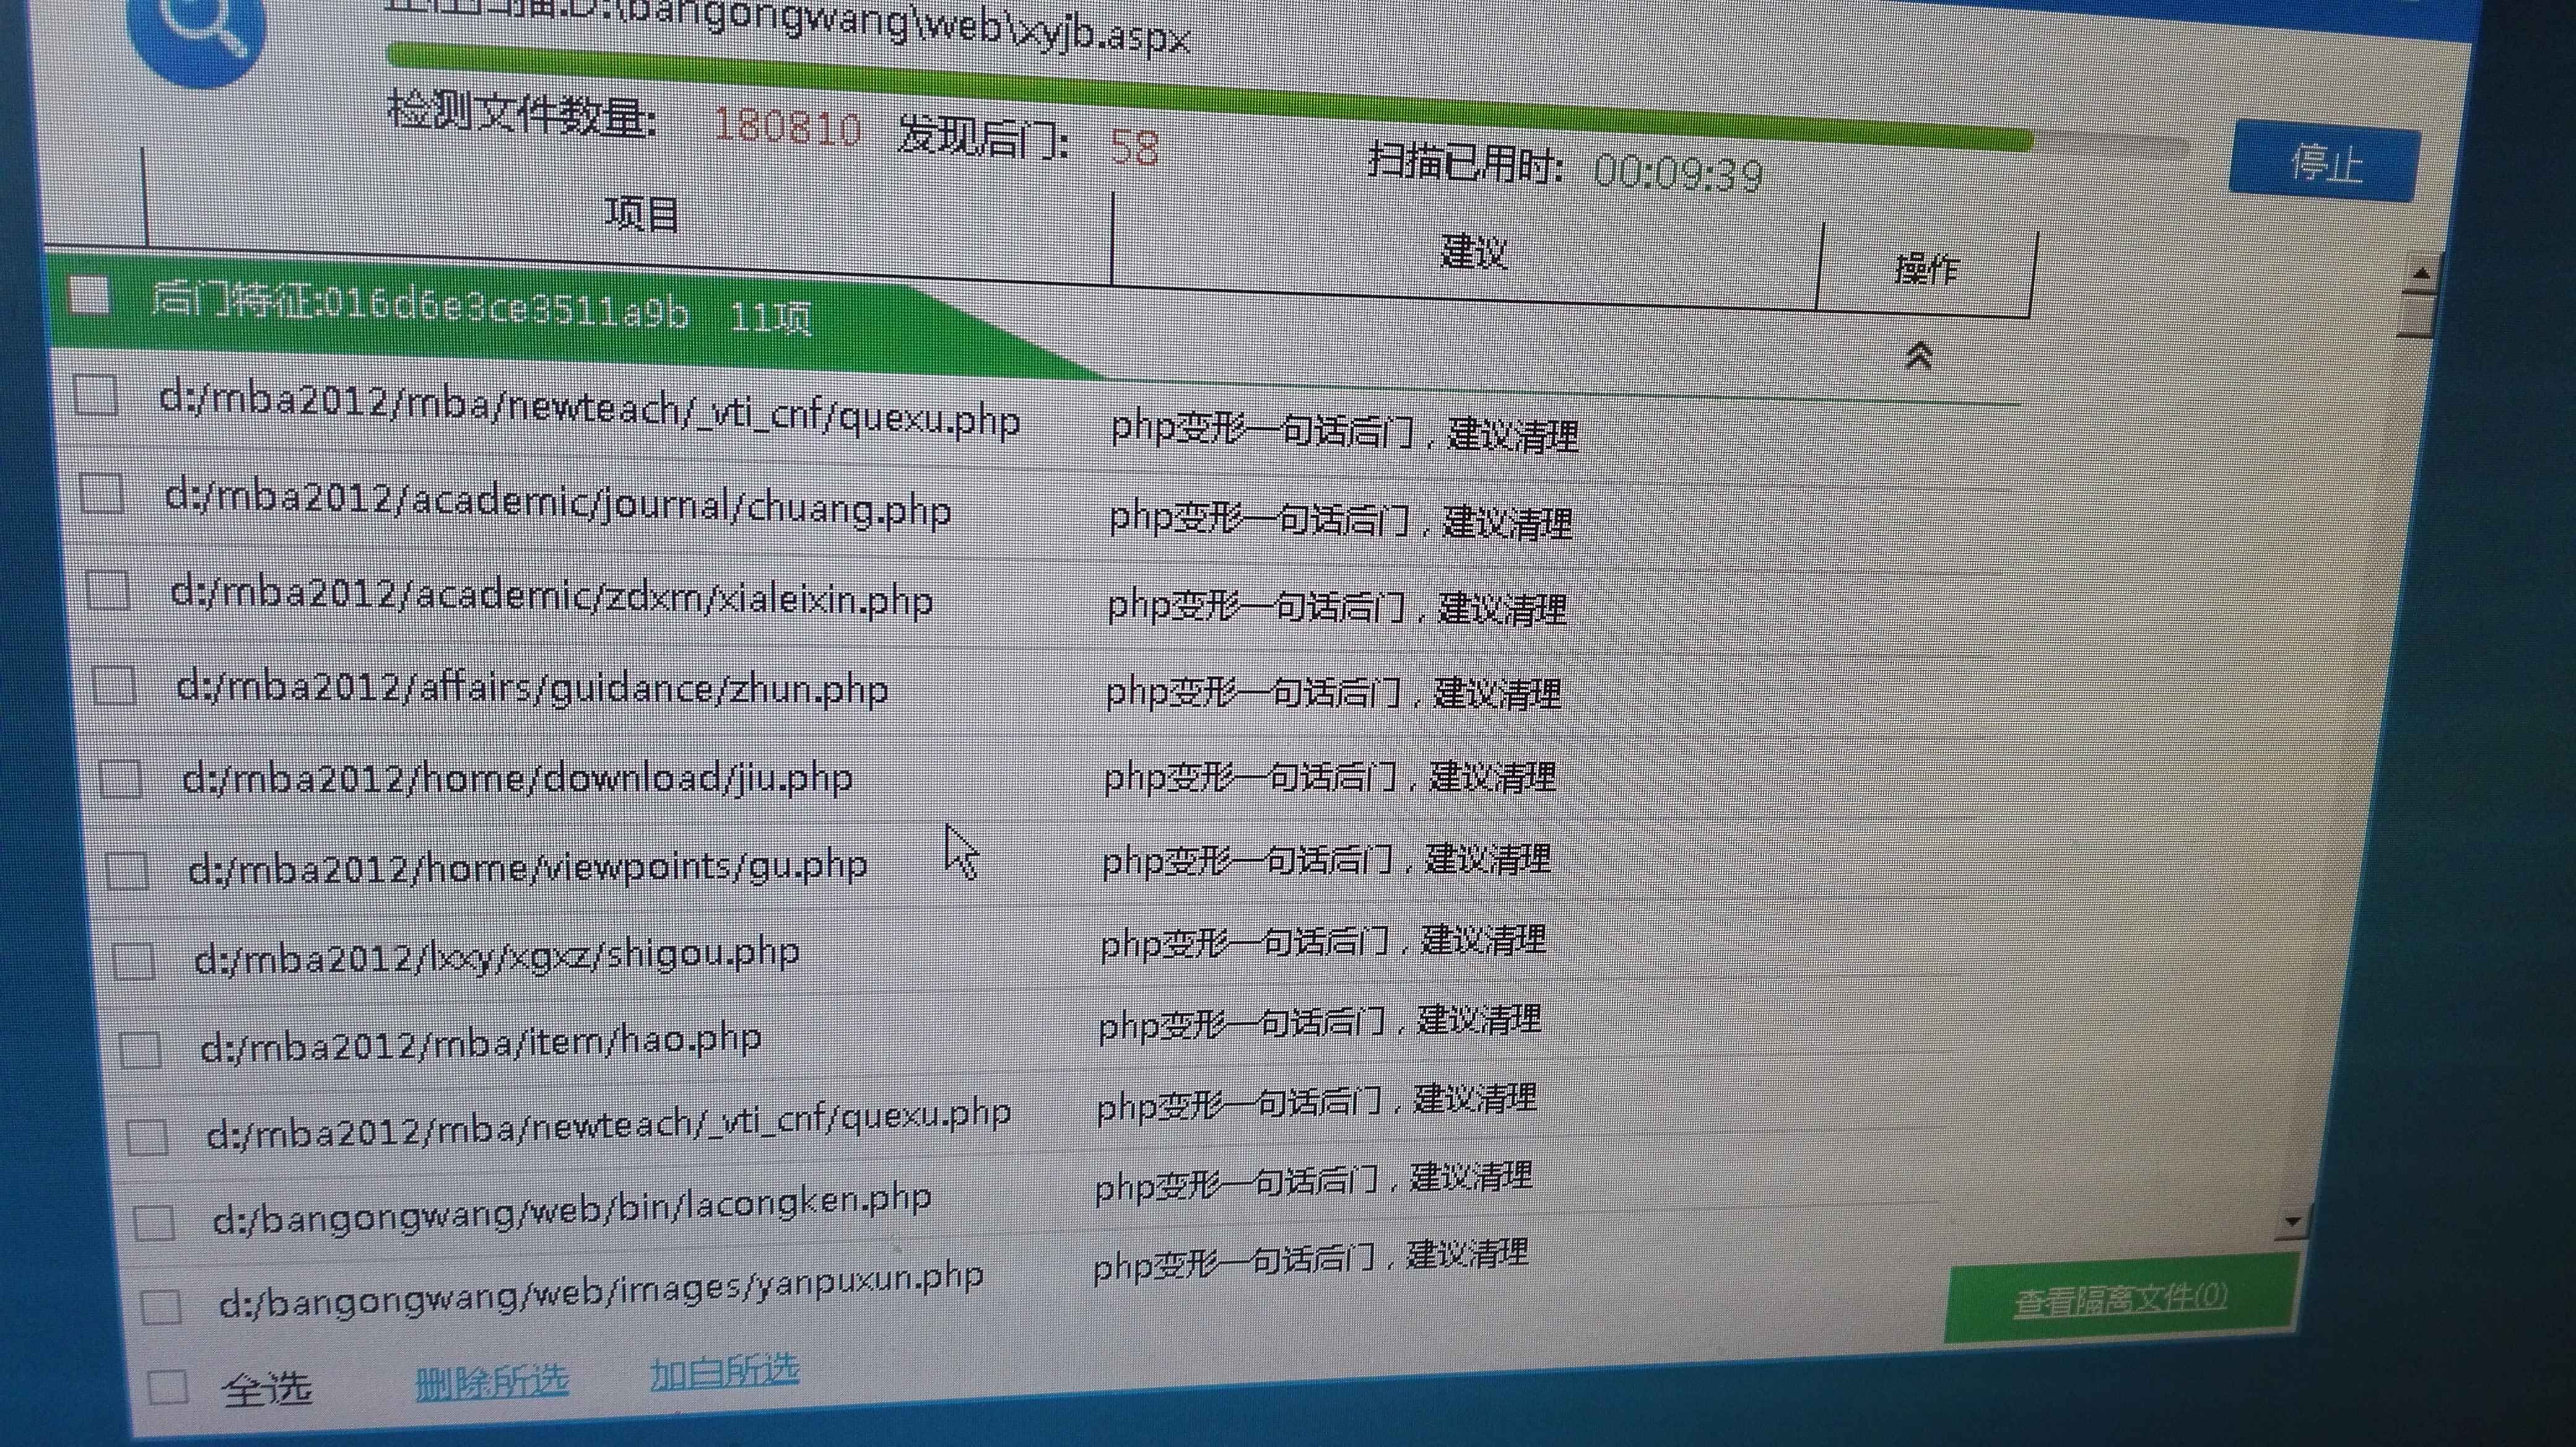
服务器木马查杀(PHP)
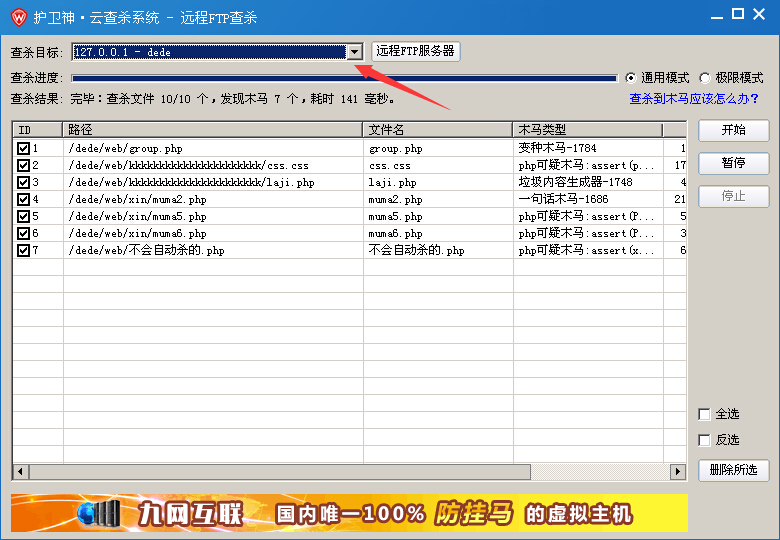
1. 安装防病毒软件. 我的服务器使用avast,效果比较好.
2. 根据木马特征扫描手动检查(手动检查需要有个人经验才能判断)
PHP Trojan木马最明显的功能是使用eval和base64_decode以及一些更危险的功能.
您可以输入以下命令进行查询
find /home/www/ -type f -name "*.php" | xargs grep "eval(" |more增强版本(在网站目录中执行):

find ./ -name "*.php" |xargs egrep "phpspy|c99sh|milw0rm|eval\(gunerpress|eval\(base64_decoolcode|spider_bc"> /tmp/php.txt
grep -r –include=*.php '[^a-z]eval($_POST' . >/tmp/eval.txt
grep -r –include=*.php 'file_put_contents(.*$_POST\[ .*\ ]);' . >/tmp/file_put_contents.txt
find ./ -name "*.php" -type f -print0 | xargs -0 egrep "(phpspy|c99sh|milw0rm|eval\(gzuncompress\(base64_decoolcode|eval\(base64_decoolcode|spider_bc|gzinflate)" | awk -F: '{print $1}' | sort | uniq
在代码中使用空格时要小心
上面的代码最终将列表输出到/ tmp目录. 请直接查看列表,然后根据情况进行操作.
3. 查找前一天修改过的PHP文件
#find -mtime -1 -type f -name \*.php修改网站的权限
本文来自电脑杂谈,转载请注明本文网址:
https://www.pc-fly.com/a/shouji/article-292271-1.html
相关阅读
发表评论 请自觉遵守互联网相关的政策法规,严禁发布、暴力、反动的言论
-

-
李林涛
烊烊棒棒哒你就是我们心中的小王子
每日福利
 360发布了第二代云防病毒引擎,可以实时“杀死”未知木马
 下载通用文档打印软件的V3.1绿色版本
 不一样的景色,微星Z170 XPOWER GAMING钛金
 如何选择可靠的计算机系统防病毒软件: 腾讯计算机管理器或360 Security Guard
热点图片
衣服什么的