使用基于Xshell的密钥连接到远程主机
电脑杂谈 发布时间:2020-05-01 08:06:38 来源:网络整理
使用Xkey基于Xshell连接到远程主机,具体内容如下
连接到远程主机时,通常有两种验证身份的方法,一种是通过用户密码,另一种是通过公钥.
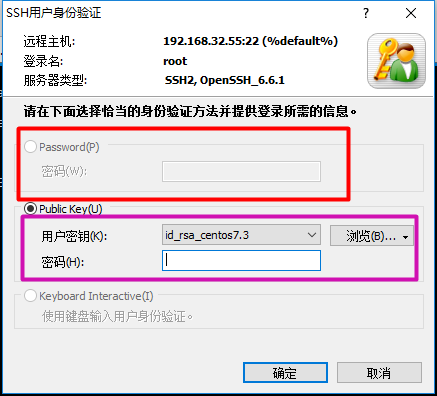
图1. xshell支持验证登录用户的方法
以下使用公钥实现连接,密钥对由工具ssh-kengen生成.

注意: 您需要在操作之前对本地计算机和目标主机执行ping操作(如果ping操作失败,可能的原因是防火墙,SELinux未关闭或网关设置有问题等)<
使用XShell,这里是XShell管理器5xshell 密钥登录,目标主机是CentOS6xshell 密钥登录,需要连接的远程主机称为目标主机.
在目标主机上安装ssh服务器并打开它
[root@node1 ~]$ yum install -y openssh-server   # 安装openssh服务端
[root@node1 ~]$ yum install -y openssh-clients  #安装openssh客户端,可以不安装
[root@node1 ~]$ service sshd start     # 临时开启sshd服务
[root@node1 ~]$ chkconfig sshd on      # 永久开启sshd服务,服务器重启也生效
[root@node1 ~]$service sshd status     # 查看sshd服务运行状态
openssh-daemon (pid 1384) 正在运行...  # 显示正在运行
生成ssh密钥对(包括私钥和公钥)

[root@node1 ~]$ (umask 0077; ssh-keygen)  # 生成ssh密钥对,并将权限设置为600
Generating public/private rsa key pair.
Enter file in which to save the key (/root/.ssh/id_rsa): # 回车
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /root/.ssh/id_rsa.
Your public key has been saved in /root/.ssh/id_rsa.pub.
The key fingerprint is:
fd:72:10:50:a6:7d:83:c7:93:d2:26:3d:12:0e:38:2f root@node1
The key's randomart image is:
+--[ RSA 2048]----+
|  .o.+  |
|  o B * . |
|  o. O % |
|  E .. O + |
|  .S o  |
|   o  |
|   . o |
|   o  |
|     |
+-----------------+
[root@node1 ~]$ cd .ssh/
[root@node1 .ssh]$ ll # 查看密钥/公钥对信息,权限都为600
总用量 8
-rw-------. 1 root root 1675 5月 21 14:26 id_rsa     # 私钥
-rw-------. 1 root root 392 5月 21 14:26 id_rsa.pub # 公钥
[root@node1 .ssh]$
修改sshd连接配置文件vim / etc / ssh / sshd_config
PasswordAuthentication no  # 不允许密码验证登录
PubkeyAuthentication yes   # 允许公钥验证登录
AuthorizedKeysFile .ssh/id_rsa.pub # 指定公钥文件路径
将ssh密钥对导出到此计算机上,建议创建一个专用于放置密钥对的目录
#]sz id_rsa
#]sz id_rsa.pub

重新加载sshd服务
[root@node1 .ssh]$ service sshd reload
重新载入 sshd:      [确定]
使用XShell连接
ssh root@IP
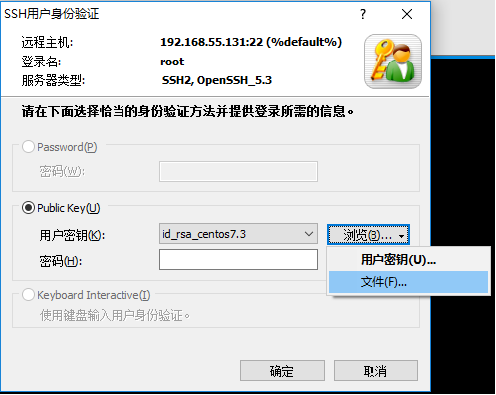

图2.选择密钥文件
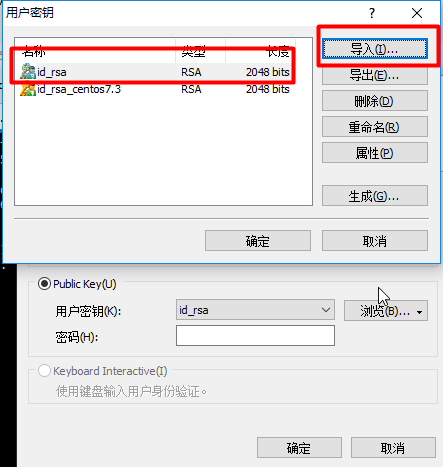
图3.导入私钥并确认
注意: 单击“确定”以重新连接
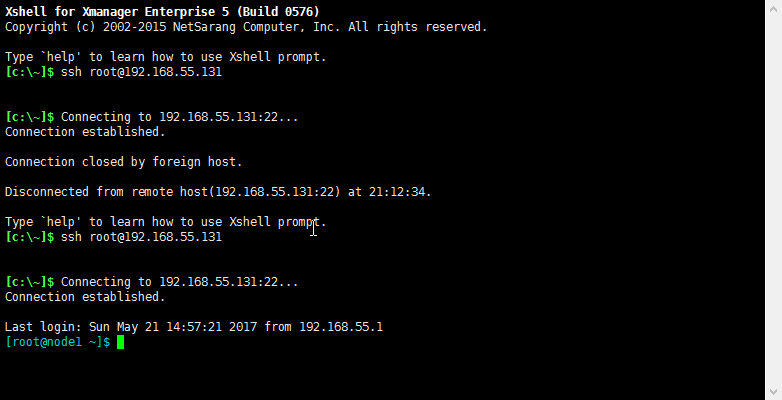
图4.成功连接
客户端使用私钥进行验证,而远程主机使用公钥进行验证.
以上是本文的全部内容,希望对大家的学习有所帮助,并希望您支持脚本编写室.
本文来自电脑杂谈,转载请注明本文网址:
https://www.pc-fly.com/a/ruanjian/article-195030-1.html
相关阅读
发表评论 请自觉遵守互联网相关的政策法规,严禁发布、暴力、反动的言论

每日福利
 最畅销的笔记本电脑是什么牌子的?
 解决方法:如果笔记本电脑的电池不耐用怎么办?
 辽宁师范大学初中信息技术版(2015年)七年级.
 在山西汇最可疑的传销的调查: 穿着一件慈善外套,主要嫌疑人获利超过10亿美元
热点图片
我们也要摆出姿态